


Be a loving person rather than in a love relationship because relationships happen one day and disappear another day. They are flowers; in the morning they bloom, by the evening they are gone. But people find it very difficult to be a loving person, a loving soul, so they create a relationship and be fool that way that "Now I am a loving person because I am in a relationship". And the relationship may be just one of monopoly, possessiveness and exclusiveness. The relationship is needed only because love is not there. Relationship is a substitute. Become alert! Relationship destroys love, destroys the very possibility of its birth.
Showing posts with label NSA. Show all posts
Showing posts with label NSA. Show all posts
Friday, 28 February 2014
Hello there, Welcome to our blog. How you all are, Hope you all doing great. On our blog you will find support for tech, hacking and social tweaks. We provide networking solutions for any type of problem. You can contact us through this blog. We will do whatever we can do for your problem.
'Optic Nerve' - Dirty NSA hacked into Webcam of millions of Yahoo users for Private Images
Once again, a new revelation showed the ugly side of the Government who are conducting Global Mass surveillance and previous documents leaked by the whistleblower Edward Snowden have defaced the US Intelligence Agency NSA, who were taking care of a number of projects like PRISM, XKeyscore, DROPOUTJEEP, and various others to carry out surveillance of millions of people.
Now, it has been revealed that the US National Security Agency (NSA) helped its British counterpart, the Government Communications Headquarters (GCHQ), to allegedly capture and store nude images and others from webcam chats of millions of unsuspecting Yahoo users, The Guardian reported.
Documents handed to the Guardian by the former NSA contractor Edward Snowden show that the GCHQ's worked with the US intelligence agency NSA on a joint project dubbed as ‘Optic Nerve’. The project carried out a bulk surveillance program, under which they nabbed webcam images every five minutes from random Yahoo users' video chats and stored them in a database.
The project didn’t target individual users; rather it targeted Yahoo webcam chats between 2008 and 2010. Indeed, the method of collection appears somewhat recklessly, and in just six months of period alone, the still images of about 1.8 million users were captured and stored in the government servers in 2008.
Instead of saving full videos, the program logged one image every five minutes from a user's chat. The document says that between 3 and 11 percent of the images taken contain "undesirable nudity."
One GCHQ document states, "It would appear that a surprising number of people use webcam conversations to show intimate parts of their body to the other person."
The collected webcam information was stored in the NSA's XKeyscore search tool, and the NSA research was used to build the tool which identified Yahoo's webcam traffic, reads the report.

GCHQ webcam spying program, Optic Nerve, was still active in 2012, according to an internal GCHQ wiki page accessed that year.
Why Images??? It is known from the revealed documents that the images were collected by the government agency, so that the group could experiment with facial recognition.
"Face detection has the potential to aid selection of useful images for 'mugshots' or even for face recognition by assessing the angle of the face," it reads. "The best images are ones where the person is facing the camera with their face upright."

The GCHQ agency staffs were allowed to display "webcam images associated with similar Yahoo identifiers to your known target", the document reads, also it states “Bulk surveillance of Yahoo users was begun” as "Yahoo webcam is known to be used by GCHQ targets."
Not Surprising, because your knotty private webcam sex session you loved and enjoyed with your lover four years back was potentially pored over by the suits at GCHQ.
Yahoo has reacted furiously and denied any prior knowledge of the webcam interception program, and said that it had no awareness of or involvement with the GCHQ collection, describing the activity as "a whole new level of violation of our users' privacy."
And a GCHQ spokesman said in a statement, "It is a longstanding policy that we do not comment on intelligence matters. Furthermore, all of GCHQ's work is carried out in accordance with a strict legal and policy framework which ensures that our activities are authorized, necessary and proportionate, and that there is rigorous oversight, including from the secretary of state, the interception and intelligence service commissioners and the Parliamentary Intelligence and Security Committee,” adding, “All our operational processes rigorously support this position."
The NSA spokesperson declined to respond saying, "As we've said before, the National Security Agency does not ask its foreign partners to undertake any intelligence activity that the US government would be legally prohibited from undertaking it."
Monday, 24 February 2014
Hello there, Welcome to our blog. How you all are, Hope you
all doing great. On our blog you will find support for tech, hacking and social
tweaks. We provide networking solutions for any type of problem. You can
contact us through this blog. We will do whatever we can do for your problem.
Have you checked our last tutorial about:
Best WhatsApp alternatives with end-to-end Encryption

WhatsApp acquisition may have had a negative impact on the reputation of the company, it seems many users are planning to switch the service and a few of them have already done it.
Mobile messaging apps often used to deliver sensitive data or used for personal and corporate communications, so the data stored by the service provider should be encrypted end-to-end, which is not yet in the case of WhatsApp.
There are many mobile messaging applications like Japan-based Line, China’s WeChat, Korea-based KakaoTalk, and Canada’s Kik, India-based Hike and many more, but they are not end-to-end encrypted messengers.
Time is loudly announcing the need to shift to some alternates which provides end-to-end encryption for communication between two devices and respect your Privacy. There are a number of solutions available includes - Telegram, Surespot, Threema, TextSecure, RedPhone etc.
1.) Telegram offers end-to-end encryption and have a 'Secret Chat' feature, that self-destruct messages after the conversation.
"We support two layers of secure encryption (server-client and client-client). Our encryption is based on 256-bit symmetric AES encryption, RSA 2048 encryption and Diffie–Hellman secure key exchange." Company states on their website.
Regular and Secret chats are encrypted, but during Secret chat no data stored on the company server.

There are a couple of more advantages Telegram brings which really are interesting. Telegram is free and an open source project, which means that the source code of the project is freely available, and according to their official website, 'Telegram has an open API and protocol free for everyone'.
Download Telegram for Android and iOS.
Download Telegram for Android and iOS.
2.) Surespot allows you to send and receive text messages, pictures and audio clip with end-to-end encryption. It uses 256 bit AES-GCM encryption using keys created with 521 bit ECDH which can only be decrypted by sender and receiver.
Unlike WhatsApp, if you delete a message, it's deleted from the recipient's phone, too. Surespot supports multiple identities on a single device. Download Surespot for Android and iOS.
Unlike WhatsApp, if you delete a message, it's deleted from the recipient's phone, too. Surespot supports multiple identities on a single device. Download Surespot for Android and iOS.
3.) Threema is not free, but a perfect alternate for WhatsApp, use end-to-end encryption and gives you all features of WhatsApp like text messaging, image sharing, and voice chat as well.
 You can also sync your contact list automatically and manually. German users have started a shift to Threema after Facebook's acquisition and the app have become top paid app on the app store in Germany. Download Threema for iOS and Android.
4.) TextSecure and 5.) RedPhone also provides end-to-end encryption for messaging and voice calls respectively. RedPhone allows you to upgrade a normal call to secure call whenever it senses the possibility to fulfil the requirements.

4.) TextSecure and 5.) RedPhone also provides end-to-end encryption for messaging and voice calls respectively. RedPhone allows you to upgrade a normal call to secure call whenever it senses the possibility to fulfil the requirements.
Friday, 14 February 2014
This tutorial is all about how you can secure your data on Cloud Storage. It will help you encrypt your data before you upload it on cloud storage using Cloud Fogger. So here we go.

Step-2: Select the folder you are using for syncing with cloud storage (Google Drive, Sky Drive, and Dropox etc.)
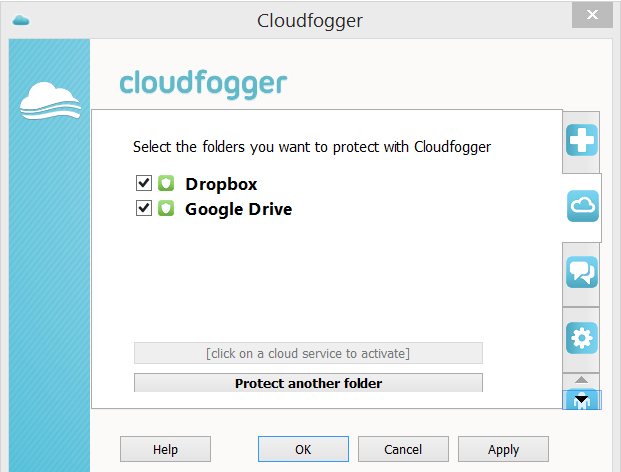


There are many Free Cloud storage providers including Google Drive, Dropbox, Box, RapidShare, Amazon Cloud Drive, Microsoft SkyDrive and many more. These services have a limitation that all data is unencrypted, or even if it is encrypted, the encryption keys are still generated by the company's software, meaning the company still has an access to your data.
So as an end user, we must think about the security and privacy of our data. We should first encrypt our files on the system level and then upload a copy of it on the cloud storage.
For this a robust and highly user friendly tool called CloudFogger is available at free of cost and for using it you even need not to be a GEEK. It provides encryption of 256 bit AES for your files.
Easy to Install and Easy to use: Follow the steps to crypt your files using CloudFogger:
Step-1: Download and Install CloudFogger from its website. Open and create an account first:


Step-3: Now you just need to drop your files into that folder. A Small Green overlay-symbol will appear on your files, i.e. Your files are now encrypted and ready to upload/sync with your Cloud storage account. That's it!
The New file extension for all encrypted files will be ".cfog", that can be accessed only if decrypted using your own CloudFogger keys.
You can also encrypt documents manually, just by right clicking it, select cloudfogger->Fogg file(s) and you can access the file yourself using a virtual drive created by cloudfogger without decrypting each file.
This client-side encryption ensures that nobody will be able to access your protected documents and files without your password. RSA private keys are stored on the Cloudfogger server to allow convenient installation of the product on several devices, but all keys are again encrypted with 256 bit AES based on the user's password and the company claims that user passwords will be never ever transmitted to their Cloudfogger servers.
Each file uses its own, unique AES key, that allows sharing files with different people, so you can add the email addresses of your friends, if you want them to allow decrypt your private document, image or etc.
For most users, finding a truly protected Cloud service can be a challenge, as many services obviously have security gaps that leave data wide open to third party attacks, leaks, or hacking.
CloudFogger is an application available for Windows, Mac, Andoird, iOS. There are many more similar tools and services that are available i.e. SpiderOak, Mozy, Carbonite, IDrive or BoxCryptor and many more.
However, CloudFogger is not an open source software, so there is an alternate available called "CryptSync", which is an open source tool for encrypting the files before uploading to cloud server and it also does not store your files on the developer’s server like CloudFogger.
Subscribe to:
Posts (Atom)
Popular Posts
-
OPEN MS-DOS Source Code Early tech fans might remember the good 'ol days of Microsoft MS-DOS, the company's first operating s...
-
 Hello folks, How are you all. Today I'm here to bring you on of the most amazing hacking news or trick you can say. So let's begin ...
-
 Hello, there again some poetry. This time i wrote this for someone who is close to my heart. Not close indeed very much close to me. I...
-
 Hello there, Do you know when you submit a page on stumble upon then what happen. Under which process it goes?. Um, No. Oh, You need not t...
-
Medium Medium, the blogging platform created by Twitter co-founder Evan Williams, launched its first mobile app this week. The app let...
-
Hello there, Welcome to our blog. How you all are, Hope you all doing great. On our blog you will find support for tech, hacking and so...
-
Google has begun a Glass at Work initiative, asking businesses how they're working with Glass, and the kinds of applications they...
-
Hello folks, this is my first post. M gonna explain about Pat and will give configuration for it with an example below. Port Address...